Who Should See What? Designing Staff Roles and Permissions in Business Software
When a business begins using a shared system, it can be tempting to give every employee the same administrator account because it is quick to set up. A permission plan starts with responsibilities, not with a list of technical switches.
That convenience creates confusion later: records can be changed by anyone, departing staff may retain access, and the owner may struggle to establish who approved a transaction.
List the actions each role performs
Write down the tasks of the owner, supervisor, finance staff, sales team, stock handler, service coordinator and any external accountant or consultant. Translate each task into actions.
- View Read only
- Create New records
- Edit Change records
- Approve Authorise
- Export Remove data
- Delete Irreversible
Separate preparation from approval
Where a workflow involves money, sensitive records or material commitments, consider whether one person should both create and approve the action.
Staff prepare
A staff member prepares a supplier payment record, quote or order.
Manager approves
An authorised manager reviews and approves before it takes effect.
Protect sensitive records and exports
Not every employee needs access to all customer records, employee information, pricing agreements or financial reports. Define who can download information and how files should be stored or shared after export.
Make access changes routine
Create a joiner, mover and leaver checklist. If shared accounts exist today, plan a controlled transition to named accounts rather than changing passwords without understanding connected tools.
New staff
Receive the role needed for their duties, and nothing extra.
Role change
Old permissions are reviewed as the new duties take effect.
Departure
Access is removed promptly, including connected tools.
Test with realistic users
Ask representatives from each role to complete normal tasks in a test environment or controlled pilot. Check whether users can do their work without seeing unrelated records or encountering excessive restrictions.
Everyone is an admin
Convenient at setup, but it creates real risk and destroys accountability.
Blocked from normal work
Staff improvise with shared logins and unsafe workarounds.
Review permissions after process changes
A role that was sensible when the business had three employees may be too broad when it grows or separates finance from operations. Revisit access when a new workflow is introduced, when a staff member takes on a new duty or when an external service provider is engaged.
Control temporary and emergency access
Sometimes a supervisor needs to grant access quickly so a critical task can continue. Define how temporary access is approved, how long it remains active and who checks that it has been removed.
Three questions to answer in advance
Emergency access should be traceable and exceptional, not a back door that becomes permanent because nobody remembers to close it.
Test both allowed and blocked actions
During acceptance testing, verify that users can complete legitimate tasks and that prohibited actions are blocked. Test direct URLs and exports where relevant, not only the navigation menu.
- Create a quote
- View assigned customers
- Submit a record for approval
- Complete daily tasks
- Approve an own exceptional discount
- Access unrelated records
- Export restricted data
- Reach an action by direct URL
Keep an access review record
A simple record can show the role, user, business reason, approving person and review date. Use it to investigate unexpected changes and support offboarding.
Five fields worth keeping
Do not treat every unusual action as wrongdoing. The context may be a training issue or an incorrectly configured process. Review the record with the relevant manager and document corrective steps.
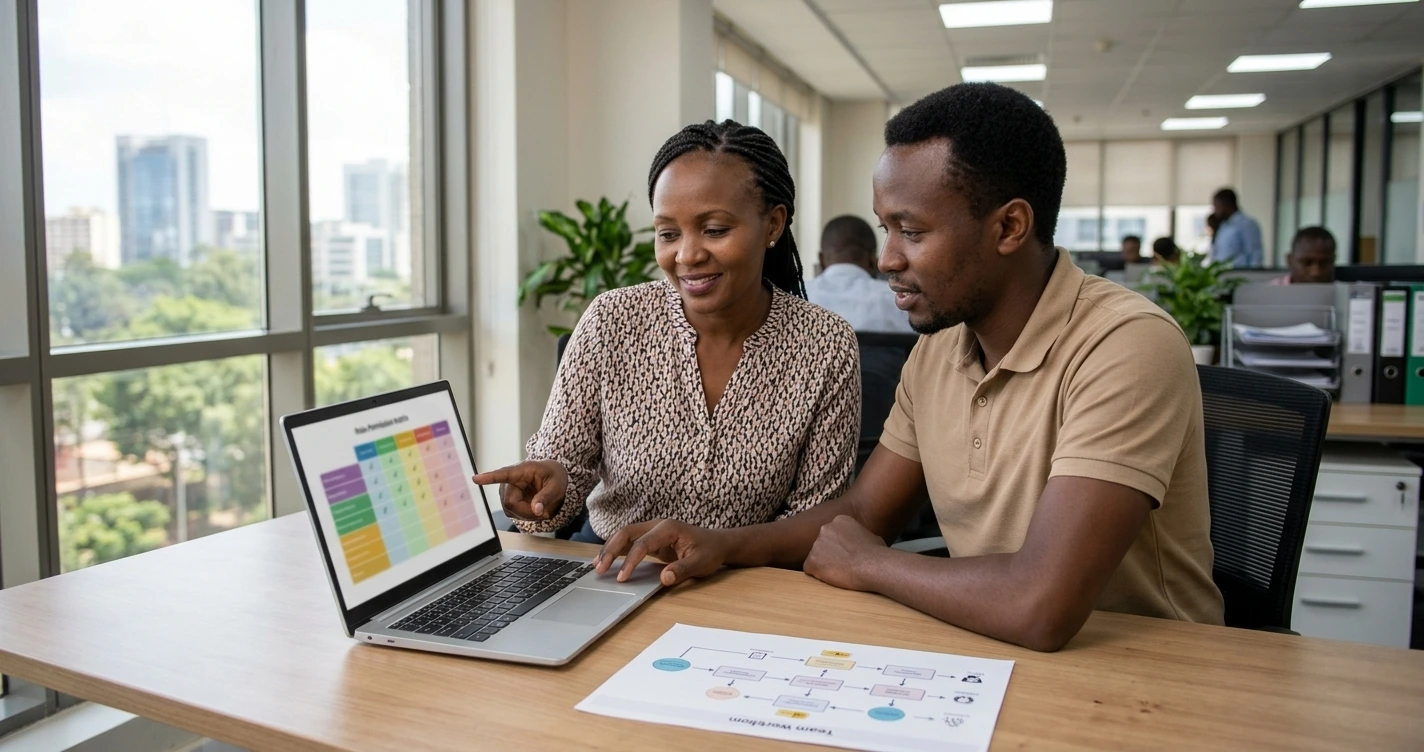
Build and test a role matrix
List the common tasks for each job role and mark whether the person should view, create, edit, approve, export or delete the relevant record. Separate preparation from approval where the business risk warrants it.
Configure the smallest set of roles that supports the real workflow. Test representative users completing permitted tasks and attempting actions they should not perform. Include exports and direct links, not only visible menu options.
Define how new staff, role changes, departures and temporary access are managed. Review permissions after process changes and at a regular interval. Keep a record of the business reason and approver for sensitive access so future reviews do not become guesswork.
A starting point, not a fixed standard
The exact matrix depends on the company's process and statutory obligations.
Frequently asked questions
Should every staff member have an individual account?
Named accounts usually improve accountability and make access changes easier than shared credentials.
How often should permissions be reviewed?
Review them when roles change and at a regular interval suited to the sensitivity and risk of the system.
Action checklist
- Each role maps to real duties.
- View, edit, approve, export and delete rights are considered separately.
- Sensitive records and exports have clear boundaries.
- Joiner, mover and leaver access changes are documented.
- Roles are tested with people who do the actual work.
Final thought
Good permissions help staff complete their work while making responsibilities visible. Design them around the real workflow, review them when people change roles and avoid treating administrator access as a convenience setting.
Designing roles for a custom system?
Stonehenge Digital KE's Business Management System service can be used to discuss role design as part of a custom system's requirements.
Explore the Business Management System Service →Interested in Business Management System?
Let's build this for your business
Replace spreadsheets, paper records, and WhatsApp chaos with a custom system built for exactly how your business works.